Repository navigation
🔒 Patch dependencies and clean up audit configuration - #373
Merged
Merged
Conversation


Apply the published Handlebars, brace-expansion, js-yaml, and shell-quote security patches. Keep release-age exceptions limited to installed patched versions and align workspace dependency ranges with their existing resolutions.

This comment has been minimized.
This comment has been minimized.
Let HTTP tests bind an available port instead of competing with CI traffic for fixed ports. Remove redundant security overrides and expired release-age exceptions, retaining only overrides needed by upstream version pins.
 Robdel12
changed the title
Vizzly - Visual Test ResultsCLI Reporter - Waiting for buildNo builds received yet for this pull request. CLI TUI - 3 changes need review
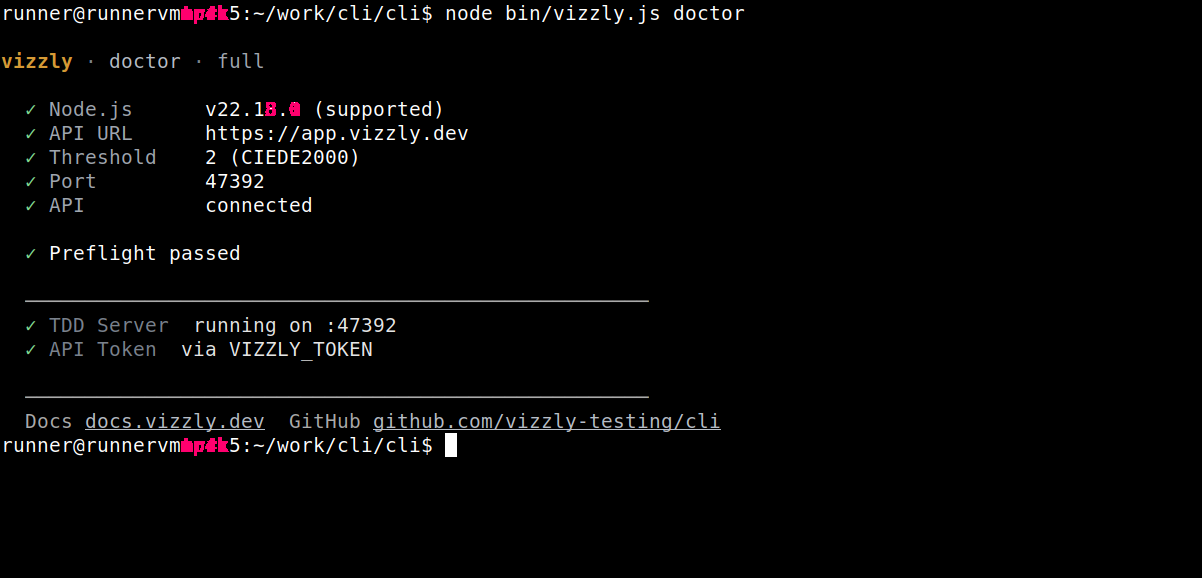
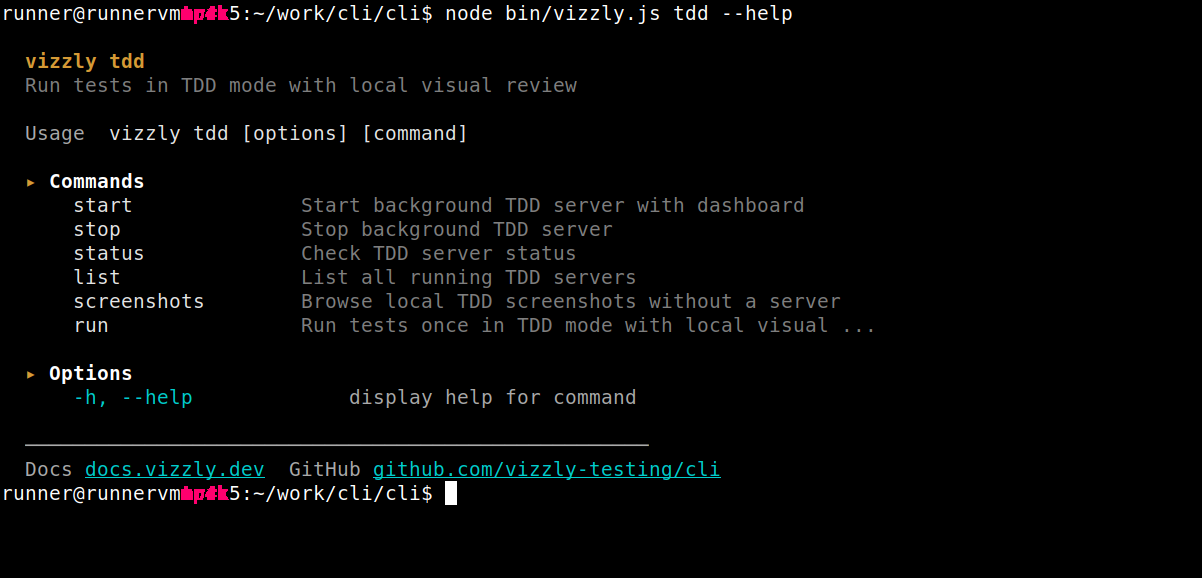
Meaningful diffs needing review (3)vizzly-doctor · 1202×578 · 0.2% diff vizzly-invalid-command · 1202×578 · 0.1% diff vizzly-tdd-help · 1202×578 · 0.1% diff
|
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment
1 participant

Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Why
The workspace audit identified command injection and denial-of-service vulnerabilities, including a critical
shell-quotefinding. The Node 22 CI job also exposed HTTP tests that failed when their hardcoded ports, 47404 and 47406, were occupied.Approach
Resolve the published Handlebars, brace-expansion, js-yaml, and shell-quote patches, and align workspace dependency ranges with their existing resolutions. Remove four redundant overrides and every release-age exception: the patched versions now satisfy the seven-day policy without exceptions.
Keep only the overrides required by concurrently's exact shell-quote pin and legacy tmp requirements in can-symlink and external-editor, with comments explaining their purpose. Concurrently 10.0.6 removes its vulnerable pin, but is still inside the release-age window. HTTP tests now bind port 0 and use the assigned address; the occupied-port test explicitly reuses the first server's port.
Evidence
The full core suite passes 1,983 tests with six skips on both Node 22.23.1 and 24.18.0, with successful CLI/reporter builds and published type checks on both. All 13 HTTP tests also pass while both CI collision ports are deliberately occupied. Frozen installation, lint, and formatting pass, and removing the overrides changes no resolved package versions.
SDK suites pass 444 unit tests and four browser integration tests. SDK and example builds pass. Reporter workflows passed Firefox CI on the dependency patch commit and 35 local Chromium desktop/mobile tests, with five intentional mobile skips.
The final audit has no critical findings and two remaining development dependency findings: braces (high) and sprintf-js (moderate). Their advertised 3.0.4 and 1.1.4 fixes are not published yet. Existing Babel 7/8 peer warnings remain, although the builds pass.